Repository navigation
test(agent): make the grant no-persistence check order-independent and pin the sign-out clear - #19184
Conversation


…d pin the sign-out clear

|
Post-merge follow-up, re: the The finding was right, and I'd independently reproduced the evasion —
Follow-up: #19184. It baselines through an ungranted refresh before snapshotting, so the storage-backed caches settle through real production code and the grant becomes the only possible delta. I checked this doesn't weaken detection — the leak shape that matters is one writing nothing on the ungranted baseline, and that is still caught under #19184 also pins Separately — thanks for the CI run. Playwright 2149 passed / 0 failed, including Still outstanding for a human, from the PR description: retire any Datadog monitor on |

|
Navigate logical layers of code changes, visualize relationships, and explore their blast radius. Important Review skippedReview was skipped as selected files did not have any reviewable changes. ⚙️ Run configurationConfiguration used: Repository: Comfy-Org/ComfyUI_frontend/.coderabbit.yaml Review profile: ASSERTIVE Plan: Team Run ID: You can disable this status message by setting the Use the checkbox below for a quick retry:
No actionable comments were generated in the recent review. 🎉 ℹ️ Recent review info⚙️ Run configurationConfiguration used: Repository: Comfy-Org/ComfyUI_frontend/.coderabbit.yaml Review profile: ASSERTIVE Plan: Team Run ID: 📒 Files selected for processing (1)
Included review availability: This review used your included allowance. Your plan provides up to 10 included reviews per hour; 6 remain after this review. Your free on-demand review promotion remains active until October 9, 2026 at 6:00 PM UTC. 📝 WalkthroughWalkthroughThe remote config tests now clear local and session storage and reset cached feature values. The invalidation test sets a session grant before invalidation and expects it to be cleared. The storage test primes two storage-backed feature values before taking snapshots. ChangesRemote config session grant
Priority: ⬇️ Low Estimated code review effort: 2 (Simple) | ~10 minutes Change: Other Suggested reviewers: Merge Risk: ⚪ Minimal · up to The test changes have no established merge-blocking risk and are ready to merge subject to normal checks. 🚥 Pre-merge checks | ✅ 7✅ Passed checks (7 passed)
✨ Finishing Touches📝 Generate docstrings
🧪 Generate unit tests (beta)
Comment |

|
Thanks for picking up the queued backports — noting one consequence, since it affects all four lines. The order-dependent test I flagged above rode along into every backport. I checked each branch rather than assuming, and all four carry the pre-fix snapshot shape:
Reproduced on Identical to One correction to something I could easily have gotten wrong: the No action needed from you right now. #19184 fixes both on |
|
@coderabbitai — no changes pushed, because this run posted no findings; it's the "Currently processing new changes in this PR" placeholder (Run ID Declining both Finishing Touches offers, deliberately rather than by omission:
Where to aim scrutiny, if you want a steer: the risk in this change is the opposite of the one it fixes. It adds a baseline Context that isn't in the diff: this fixes a test merged in #19074, where a Also worth knowing for blast radius: the affected test was backported to |

🌾 Fallow: ✅ PassedFallow audits the diff for duplication, complexity and dead code. It gates on new findings only, so when the audit completes, a red is something this PR introduced or moved — never inherited backlog. A red can also mean the audit itself did not finish; the details below say which happened. No new findings in the changed files. Reproduce locally# the base the gate compared against
npx fallow audit --root . --quiet --format json \
--changed-since e51671a5dbde87fa8799d64d7b1c3c7aa10ef23a
Full docs: ADR-DEVEX-LINT-0015 🎨 Storybook: ✅ Built — View Storybook🧩 Custom Nodes Ecosystem Matrix: 🟡 Withheld — could not measureExecutes the frontend JS of every registry pack that ships any, against this change, in both renderers. The eight This candidate changes nothing the matrix measures, so every expensive stage was skipped. Reproduce locally# build one shard's fixture, then run it
python3 scripts/registry-census/build_matrix.py --shard 1/4
MATRIX_RENDERER=vue MATRIX_VUE=1 \
npx vitest run --config vitest.matrix.config.mts
Full docs: scripts/registry-census/README.md |
|
Acknowledged on all the resolved threads — replying once rather than on each, since the disposition is the same. Tracking them in FE-3060 with acceptance criteria is the right call; nothing further needed from me on those. One reconciliation note so the two efforts don't overlap or leave a gap. FE-3060's title covers auth phase, settle lifecycle and refresh retries, which maps cleanly onto the production-side residues: the unbounded grant retention under a sustained outage, Two findings from the same review are test-side and may fall outside that scope. Both are already fixed in #19184:
I've left the same note on FE-3060 so it's visible wherever the work gets picked up. Also relevant to the backports you completed: both issues rode into all four release lines. I verified each branch rather than inferring, and reproduced the flake directly on
Release CI is green on all four, so nothing surfaces this until someone debugs a single test there. Say the word and I'll open the four backports once #19184 lands, or leave it to whatever queue handled #19175–#19178. |

|
@coderabbitai — no changes pushed: this review reports "No actionable comments were generated", with 7/7 pre-merge checks passed and merge risk Minimal. Nothing to address. Declining both Finishing Touches offers, deliberately:
Your walkthrough summary is accurate, which is worth saying since the subtlety is easy to miss: "performs an ungranted refresh before taking storage snapshots, then checks that a granted refresh leaves both stores unchanged." That ordering is the entire fix — the baseline has to run before the snapshot so the storage-backed billing caches settle through real production code, leaving the grant as the only possible delta. State of this branch: rebased on merged It's still marked draft. Two things are queued behind it, so it's worth a look when someone has a moment:
|
 github-actions
Bot
added
the
risk:high

Codecov Report✅ All modified and coverable lines are covered by tests. @@ Coverage Diff @@
## main #19184 +/- ##
==========================================
+ Coverage 84.15% 84.65% +0.50%
==========================================
Files 3226 2337 -889
Lines 155844 134037 -21807
Branches 42175 34548 -7627
==========================================
- Hits 131146 113469 -17677
+ Misses 22970 20214 -2756
+ Partials 1728 354 -1374
Flags with carried forward coverage won't be shown. Click here to find out more. 🚀 New features to boost your workflow:
|
|
Re: "Implemented in #19219" — I checked that branch against the two test-side findings, running them on 1. The order-dependent test survives. It still snapshots storage before the first authenticated refresh: Marginally worse than on 2. The sign-out grant clear is still unpinned. Deleting To be clear, this isn't a criticism of #19219's scope. Bounding transient grants to 15 minutes directly closes the unbounded-retention residue I flagged, and verifying 3. They conflict. Suggestion: fold #19184 into #19219 and close #19184. It's 13 lines in a file you're already editing, and it means the fix rides the same four backports instead of needing a second round. The substance: run an ungranted Alternatively I'll rebase #19184 onto your branch and keep them separate. Your call — I won't push to your branch either way. |
|
Correction and an update — #19219 has moved since my last comment ( Good news first: the settle-lifecycle residues I raised are genuinely closed. Confirmed in the new
Plus tests for each, including The two test-side findings still stand on the new head, re-run just now: And the sign-out clear is still unpinned — deleting Neither is a criticism of #19219's scope — both are orthogonal to what it set out to fix. The offer stands: fold #19184's 13 lines in (it's a file you're already editing, and it rides the same four backports), or I rebase #19184 onto your branch. Still haven't touched it. |

…sistence-test-isolation

# Conflicts:
#	src/platform/remoteConfig/refreshRemoteConfig.test.ts
 christian-byrne
added
the
cursor-review

|
Refreshed onto current Local exact-head evidence: 24/24 focused tests pass, the previously order-dependent test passes alone, and format/lint/typecheck pass (lint reports only pre-existing warnings outside this one-file diff). Marked ready and triggered current-head review. |
christian-byrne
added
agent

 christian-byrne
left a comment
christian-byrne
left a comment
There was a problem hiding this comment.
Exact-head self-review at 91e0c0c98: the diff is limited to one test file. The baseline refresh now occurs before storage snapshots, so the grant is the only possible delta; the invalidation case seeds a grant and asserts that identity invalidation clears it. No production behavior, API, performance, security boundary, docs, or browser-visible flow changes. Full-file and isolated-order tests pass, and the existing mutation evidence remains the causal coverage proof.
|
Verified your rebase at
Your summary is accurate. Nothing further from me. A correction I owe you, because it's mine and it's load-bearing. Earlier in this thread I reported that deleting the sign-out grant clear "leaves 121/121 green" and "126/126 green" — i.e. that the invalidation path was unpinned. At least one of those was a false negative, and I can't fully stand behind either. My mutation script located the line by counting, then removed it with a I caught it here only because the numbers stopped making sense: the test visibly seeds The fix on my side is a harness that verifies the file changed before trusting the run — which is the same lesson this PR is about, one level up: an assertion that can't fail is worse than no assertion, whether it's in a test or in the tool you're using to check the test. Sorry for the noise on #19074 and #19219. The order-independence and no-persistence findings were separately reproduced and stand; the "invalidation unpinned" claim should be struck. My local copy is still at the pre-rebase |


There was a problem hiding this comment.
🔍 Cursor Review — Consolidated panel
Triggered by @christian-byrne.
Round 2 — ledger: 3 prior finding(s) across 1 round(s) (0 never answered).
Found 10 finding(s).
| Severity | Count |
|---|---|
| 🟠 High | 3 |
| 🟡 Medium | 7 |
Panel: 8/8 reviewers contributed findings.
The finding(s) below could not be anchored to a line the reviewed diff carries, so they are reported here instead of inline:
.github/workflows/workshop-workflow-sweep.yaml:24— 🟠 High —queue: maxis not a recognized key underconcurrency— GitHub Actions accepts onlygroupandcancel-in-progressthere, and an unknown key fails workflow validation ("Unexpected value 'queue'"), so neither the six-hourly free sweep nor the daily paid run would ever execute. The failure surfaces as a repo-level invalid-workflow error rather than a failed run, so nothing here would ever go red to tell you.Raised by 3 of 8 reviewers (claude-opus-5-thinking-max edge-case, kimi-k3-max adversarial, kimi-k3-max edge-case).
src/platform/workspace/stores/workspaceAuthStore.ts:211— 🟠 High —switchSessionWorkspacesetscurrentWorkspace.value = nullbefore awaiting the confirming/workspaces/currentcall and leaves it null when that call is refused or returns a mismatched id. BecauserequestScope()omitsX-Comfy-Workspace-IDfor a null workspace, and an absent header means the personal workspace server-side, any request racing the switch — or any request after a failed switch or afterdropDeniedWorkspace— silently reads and writes in the personal workspace instead of erroring. Keep the previous scope until the new one is confirmed, and represent "unresolved" distinctly from "personal" so those requests fail closed.Raised by 3 of 8 reviewers (claude-opus-5-thinking-max adversarial, kimi-k3-max adversarial, kimi-k3-max edge-case).
src/platform/auth/session/cloudWebSessionStore.ts:180— 🟠 High —requestScope()awaits the session-readiness promise with no timeout and no caller signal, andapi.fetchApidoes not create its 60-second controller until aftergetWebSessionSend()has awaited this, so a bootGET /auth/sessionthat never settles hangs every API request and the workspace auth gate indefinitely. The token rail bounds the equivalent wait (waitForAuthInitialization, 10s cap); givereadya comparable deadline so a stalled probe degrades to an error rather than silently freezing all traffic.Raised by 2 of 8 reviewers (gpt-5.6-sol-max adversarial, claude-opus-5-thinking-max adversarial).
src/platform/auth/session/cloudWebSessionStore.ts:197— 🟡 Medium — WhenreadWebSessionreports that the cookie now belongs to a different account,rereadFordiscards the result and returns undefined, leaving the storesigned_inas the previous user with that user's CSRF token and workspace. Every unsafe request then repeats the stale-token 403-and-reread cycle until the next heartbeat (indefinitely while the tab is hidden), while safe requests already run under the new cookie with the old workspace metadata; propagate the identity change intoidentityinstead of dropping it on the floor.Raised by 1 of 8 reviewers (gpt-5.6-sol-max adversarial).
src/stores/authStore.ts:244— 🟡 Medium — On the web-session railgetAuthHeader()short-circuits togetUserAuthHeader(), returning only the account-scoped Firebase bearer with no workspace header and no CSRF token, so any caller that authenticates its own request with this instead of going throughfetchApi/fetchOnWebSessionloses team scoping and resolves against the personal workspace.getWorkspaceAuthHeaderhas no session branch at all, so the axiosworkspaceApicalls (members, invites, billing mutations) still mint Firebase/workspace tokens — worth confirming which callers remain on that path, since the session and the local Firebase user can name different accounts.Raised by 2 of 8 reviewers (claude-opus-5-thinking-max adversarial, gpt-5.6-sol-max adversarial).
apps/billing-web/src/session/unifiedBillingSession.ts:158— 🟡 Medium — The identity subscriber clearsworkspace.valueon every state push, not just on an account change, so a routine session republish for the same user (refresh, cross-tab sync) blanks the resolved workspace for a full/workspaces/currentround trip:livePhasegoes undefined,billedScopeblanks the UI, andscopeSource.getScope()returns undefined for anything issued in that window — the same headerless window the rebind clear on line 139 opens. Gate this clear on the user id actually changing (asresolveWorkspace()already does for the binding), and confirmcreateCredentialedBillingTransportblocks an unresolved scope rather than sending the request with no workspace header.Raised by 2 of 8 reviewers (claude-opus-5-thinking-max adversarial, kimi-k3-max adversarial).
apps/billing-web/src/session/unifiedBillingSession.ts:126— 🟡 Medium —fetchWorkspaceaccepts whatever/workspaces/currentreturns without checking it matches the requested binding, so ifX-Comfy-Workspace-IDis dropped by a proxy or ignored by the backend, the personal workspace is stored as the resolved billing scope and checkout charges it while the entry link still names the team.workspaceAuthStore.switchSessionWorkspace, added in this same PR, guards exactly this case (current.data.id !== workspaceIdthrowsworkspace-switch-mismatch); apply the same comparison here and treat a mismatch as a resolution failure.Raised by 1 of 8 reviewers (claude-opus-5-thinking-max adversarial).
apps/billing-web/src/views/CheckoutView.vue:471— 🟡 Medium — TheREACTIVATION_CONFIRMATION_REQUIREDbranch re-quotes with no promotion code, and the applied code lives only on the preview it is about to replace, so a customer who applied a valid promo and then hit server-side reactivation confirmation silently loses the discount: the new preview is undiscounted andbuildSubscribeRequestreadspromotion_codeoff that preview, so the subscribe carries none. Pass the code through the re-quote (preview.value?.promotion_code) or retain it in component state.Raised by 1 of 8 reviewers (claude-opus-5-thinking-max edge-case).
apps/billing-web/src/views/CheckoutView.vue:232— 🟡 Medium —teamCheckoutPlanfalls back tomonthlyUsd = 0/monthlyCredits = 0whenever the stop is missing fromplans.value?.team_credit_stops, and team plans arepricedByQuote: false, so the confirm renders "$0 USD / mo" and "0 credits" for as long asusePlans()is still loading (the only load gate isquoting, which watches the preview, not the plans) and forever if the link names a stop the catalog no longer lists — with Pay enabled throughout, so a customer can submit a charge against a page showing $0. Gate the confirm on the plans read, or price the stop from the quote rather than failing open to zero.Raised by 2 of 8 reviewers (claude-opus-5-thinking-max edge-case, kimi-k3-max adversarial).
apps/website/src/components/workshop/WorkflowPlayground.vue:303— 🟡 Medium —WorkflowCreditsGuardrenders its default slot only when the gate resolves to'run', andworkflowCreditsGatereturns'run'only whilebusyor funded, so wrapping all ofWorkflowRunControlsmeans a zero or refused balance in a non-busy terminal phase (e.g.interrupted) removes Reconnect and Dismiss entirely — precisely the state whose own footer copy warns the run "may still be running on Cloud and using credits", leaving the user no way to reconnect or clear it. Gate only the start affordance, not the whole control block.Raised by 1 of 8 reviewers (claude-opus-5-thinking-max edge-case).
|
The exact-head Cursor panel completed, but its ten findings are outside this PR. |
|
Independently confirmed the scope call — dismissing ten automated findings is worth a second pair of eyes rather than taking on trust.
And zero matches across every path family the panel named:
So the ten findings are genuinely outside this diff, and none of them could be introduced by it. Your read is right, and pulling unrelated production changes in to satisfy a panel that mis-scoped its input would be the wrong fix. One item that postdates your comment: Nothing outstanding from me. Head |


|
Thanks @DrJKL. One thing worth flagging before merge: the head moved after your review. You reviewed
Each edit confirmed applied before its run (M2 Branch contribution is still exactly one file against current So the scope conclusion from the Cursor-panel thread holds unchanged too. Nothing outstanding from me. If the approval did go stale on the merge commit, this is the evidence for re-approving |
github-actions
Bot
added
risk:medium

|
@christian-byrne Successfully backported to #19395 |
|
@christian-byrne Successfully backported to #19396 |
|
@christian-byrne Successfully backported to #19397 |
|
@christian-byrne Successfully backported to #19398 |
 comfy-pr-bot
removed
the
needs-backport

…y-Org#20742) *PR Created by the Glary-Bot Agent* --- ## Summary Adds a regression guard for FE-3332 and FE-2812 (Pylon Comfy-Org#19184). From Sep 9 to Sep 30, users' Imported tab on Cloud showed every base-template input. The cause: Comfy-Org#15381 moved the Assets panel to `useAssetsQuery` without `include_public=false`. Cloud ingest defaults that parameter to `true`, so the shared template-input catalog came back with the user's own uploads. Comfy-Org#18633 restored the parameter (backported as Comfy-Org#19542, shipped in `cloud/v1.55.15`), but no test pinned it. The new `@cloud` spec `browser_tests/tests/sidebar/assets-imported-public.spec.ts` stubs `/api/assets` to match the server default: it returns public assets unless the request sends `include_public=false`. It then asserts: - the Imported tab shows only the user's own input; - the Generated tab shows no other user's assets; - every panel request (`tags_any=input` and `tags_any=output`) sends `include_public=false`. Test only, no production code changes. Companion PR in `Comfy-Org/cloud`: Comfy-Org/cloud#12841. It pins the same contract at the ingest handler and in the daily staging/prod e2e. ## Verification - Ran `pnpm build:cloud`, served `dist/` from local ComfyUI (`--cpu --multi-user` plus devtools, same as CI), then `pnpm exec playwright test --project=cloud browser_tests/tests/sidebar/assets-imported-public.spec.ts`: **2 passed (~12s)**. - Negative control: I removed `include_public: false` from `BASE_PARAMS` in `useAssetsQuery.ts` and rebuilt. **Both tests fail.** `template_sample_a` and `published_render` cards render, `toHaveCount(0)` gets 1, and the parameter assertion fails. Then I restored the line. - oxfmt, oxlint (type-aware), `typecheck:browser` and the server-facts gate passed via pre-commit. - Screenshots come from the same spec: with the fix, the Imported tab shows only `my_upload`. With `include_public` removed, extra template-input cards appear. ## Screenshots 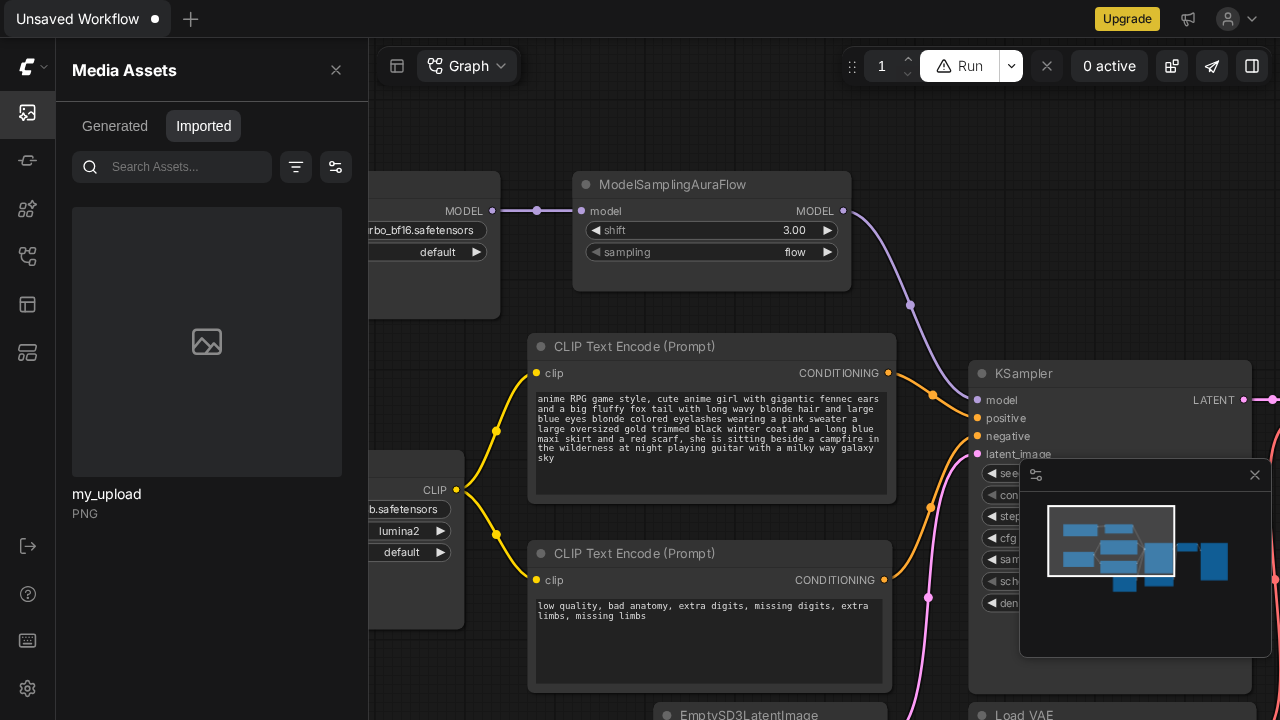 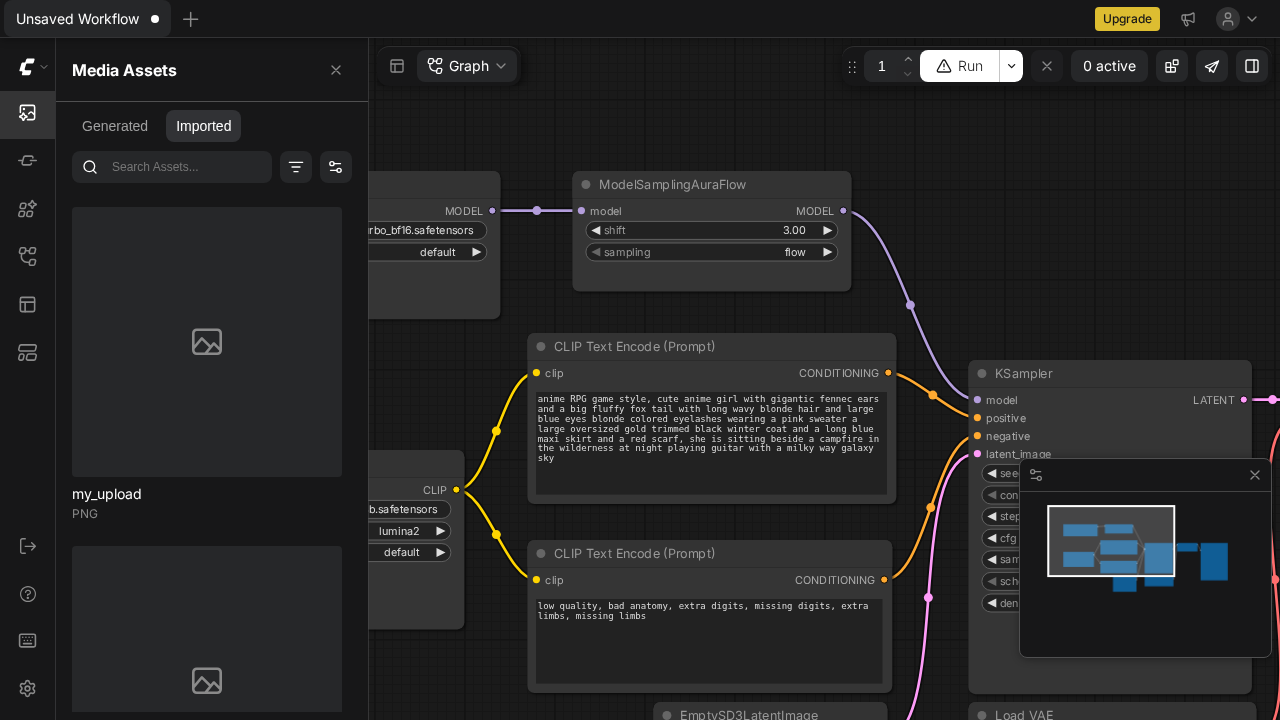 --------- Co-authored-by: Glary-Bot <glary-bot@users.noreply.github.com>




PR Created by the Glary-Bot Agent
Test-only follow-up to #19074, which stopped Agent access granted to one signed-in account from persisting for another account.
What this changes
The grant-persistence regression test now runs independently of test order. Each test clears browser storage and resets the module-scoped cached feature values. The persistence case primes only the two feature flags that are intentionally stored, takes complete storage snapshots, and performs one authenticated refresh with Agent access enabled. Any new persisted key still changes the snapshot and fails the test.
The identity-invalidation test now seeds both the transient Agent grant and its expiry time before checking that
invalidateRemoteConfig()clears them. This prevents either assertion from passing on empty setup.No production code changes.
Regression evidence
agent-in-app-experiencesession_whitelistVerification
src/platform/remoteConfig/refreshRemoteConfig.test.ts: 24/24 passedsrc/platform/remoteConfig: 24/24 passed