Repository navigation
[backport cloud/1.51] fix(billing): use user-scoped auth header for customer endpoints - #15908
Merged
Merged
Conversation


) ## Why this is needed Users who sign in with a **Comfy API key** (no Firebase session) cannot use any user-scoped billing surface: credit balance never loads, credit purchase fails, and the usage/events feed errors out. The same flows work fine for Firebase-authenticated users. ## Root cause The user-scoped `/customers/*` endpoints accept either a Firebase ID token (`Authorization: Bearer …`) or a Comfy API key (`X-API-KEY`) — the backend resolves the user identity from whichever credential is presented. But on the frontend, most call sites requested **only** the Firebase header: - `authStore.fetchBalance()` → `getFirebaseAuthHeader()` → returns `null` for API-key sessions → throws `userNotAuthenticated` - `authStore.addCredits()` → same - `customerEventsService.fetchEvents()` → same → "Authentication header is missing" Only `createCustomer()` had an inline API-key fallback, so the customer record could be created, but every subsequent user-scoped call failed. The credential choice was duplicated ad hoc per call site instead of being defined once. ## How we change it Add one auth-header accessor on `authStore` that encodes the credential rule for user-scoped endpoints, and use it at every user-scoped call site: ```ts const getUserAuthHeader = async (): Promise<AuthHeader | null> => currentUser.value === null ? useApiKeyAuthStore().getAuthHeader() // API-key session → X-API-KEY : await getFirebaseAuthHeader() // signed-in session → Firebase token ``` - `fetchBalance`, `addCredits`, `createCustomer`, `accessBillingPortal`, and `customerEventsService` now all go through `getUserAuthHeader()`. - No frontend-derived identity or state: the frontend only forwards the stored credential; the server keeps deciding whose balance/events/purchase it is. - Workspace-scoped calls are untouched — this helper is never a workspace token. ## AS IS API-key session: the balance/customer calls fail with a missing auth header, so the app treats the session as unauthenticated and bounces the user back to the login dialog. 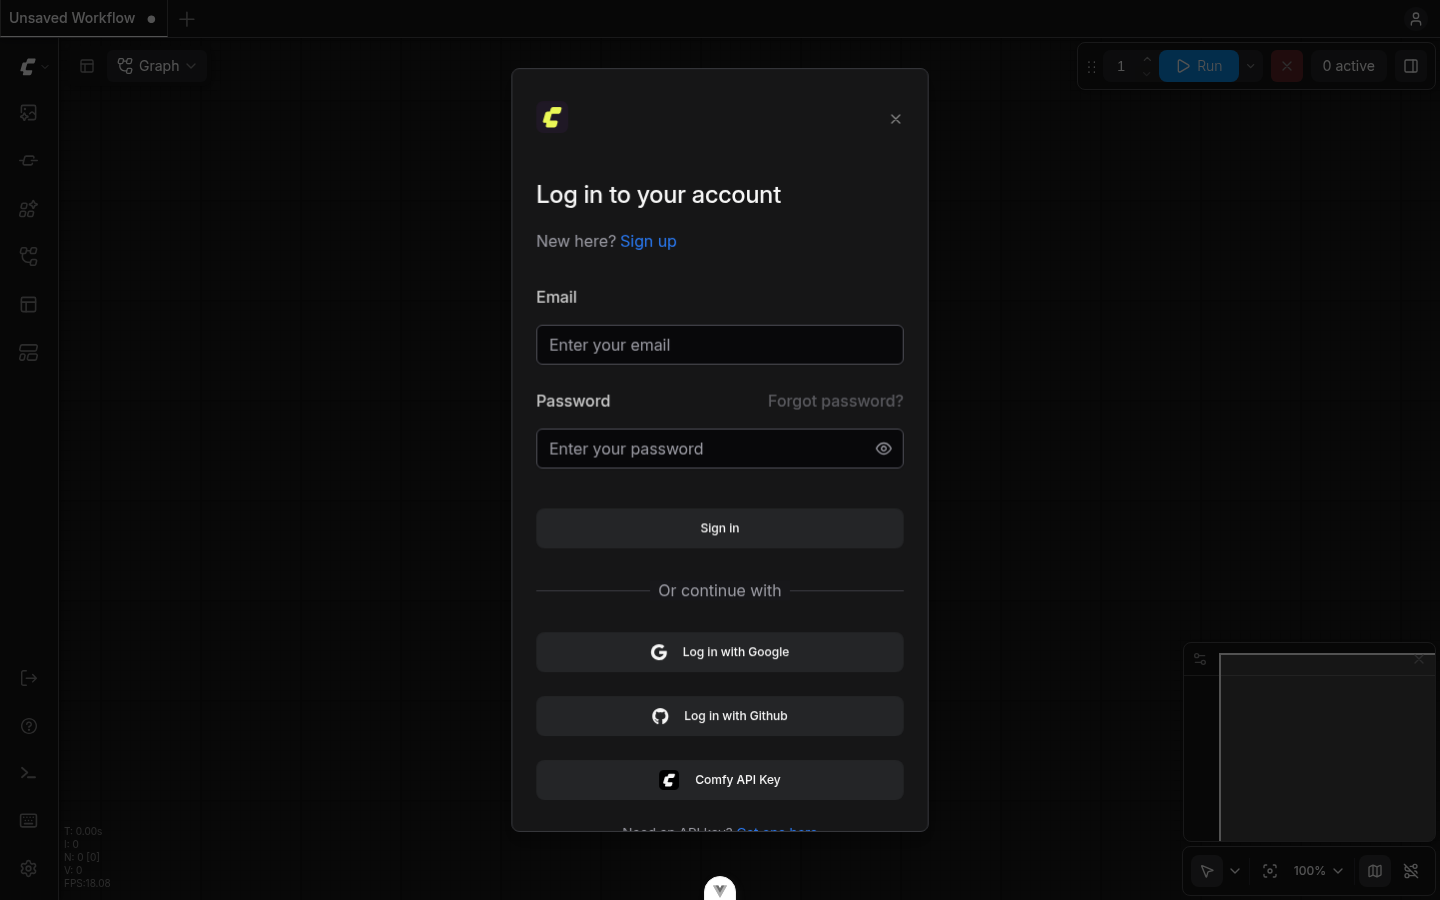 ## TO BE Same API-key session: user popover renders as authenticated and the credit balance loads (served by the backend from the `X-API-KEY` credential). 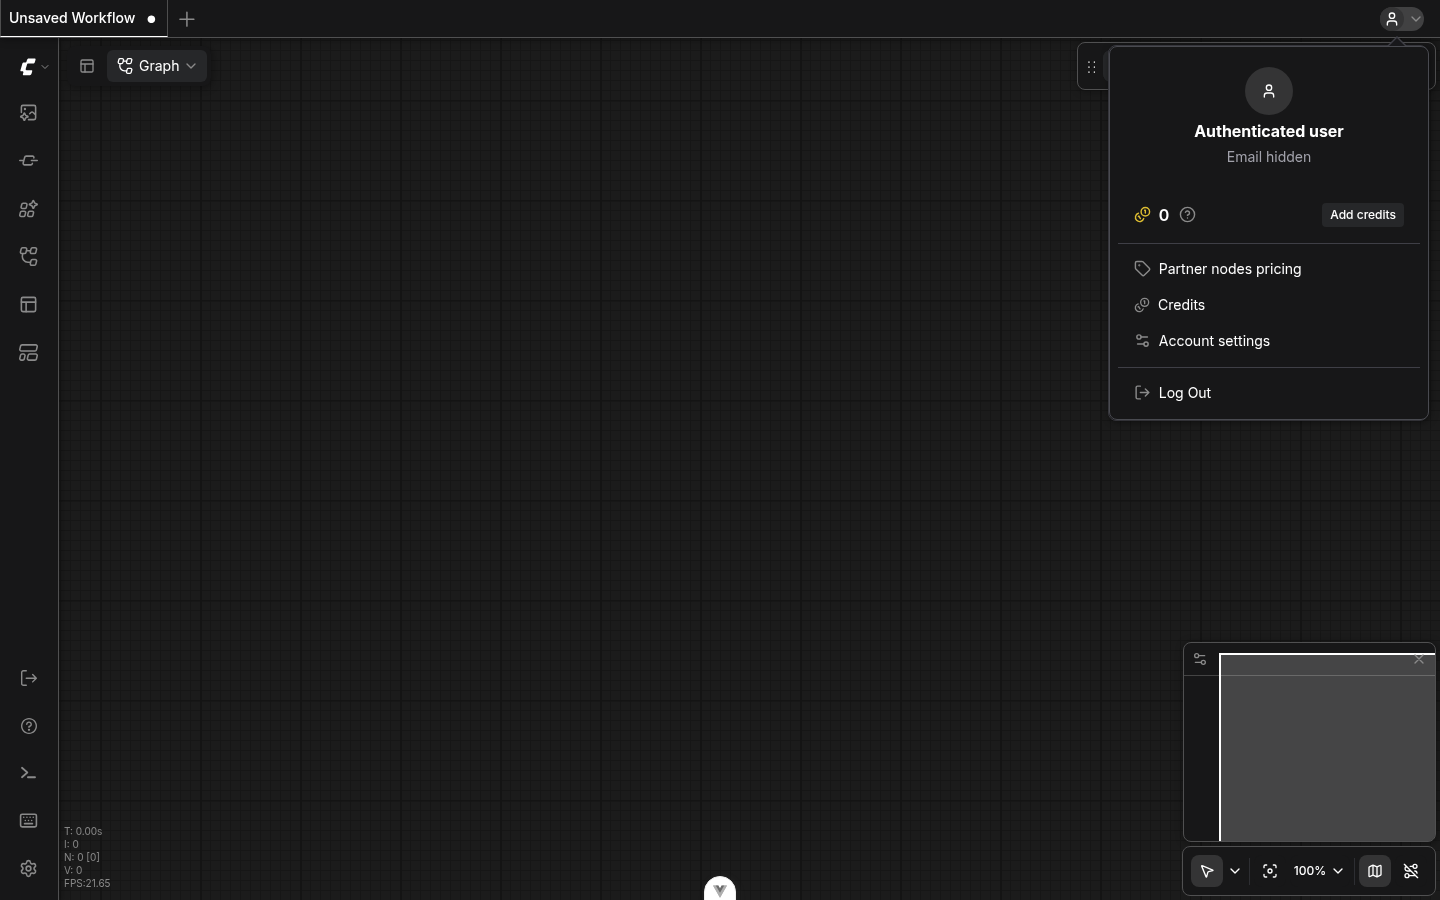 ## Tests - New unit tests: API-key session sends `X-API-KEY` for `fetchBalance` / `initiateCreditPurchase`, Firebase token still preferred when signed in, and `userNotAuthenticated` is thrown when neither credential exists (`src/stores/authStore.test.ts`). - `customerEventsService.test.ts` updated to cover the shared accessor. - `accessBillingPortal` covered both ways: an API-key session sends `X-API-KEY` to `POST /customers/billing`, and `userNotAuthenticated` is still thrown when neither credential exists. Without it, Invoice History and Manage billing in the Credits panel stayed unreachable for API-key sessions even though the backend accepts the key there. - 127/127 tests pass across both touched suites.

comfy-pr-bot
enabled auto-merge (squash)
August 25, 2026 17:37
 dosubot
Bot
added
the
size:L

Contributor
🎨 Storybook: ✅ Built — View Storybook🎭 Playwright: ✅ 1830 passed, 0 failed · 1 flaky📊 Browser Reports
|
 github-actions
Bot
added
the
risk:R3

dante01yoon
approved these changes
Aug 25, 2026

Codecov Report❌ Patch coverage is
@@              Coverage Diff              @@
##             cloud/1.51   #15908   +/-   ##
=============================================
  Coverage              ?   81.59%
=============================================
  Files                 ?     1885
  Lines                 ?   117831
  Branches              ?    37278
=============================================
  Hits                  ?    96145
  Misses                ?    21215
  Partials              ?      471
Flags with carried forward coverage won't be shown. Click here to find out more.
🚀 New features to boost your workflow:
|
 huang47
added
the
risk:xhigh
 ChatGPT Codex Connector
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment




Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Backport of #15891 to
cloud/1.51Automatically created by backport workflow.